
4 posts tagged with "Application Security"

Application Security

View All Tags

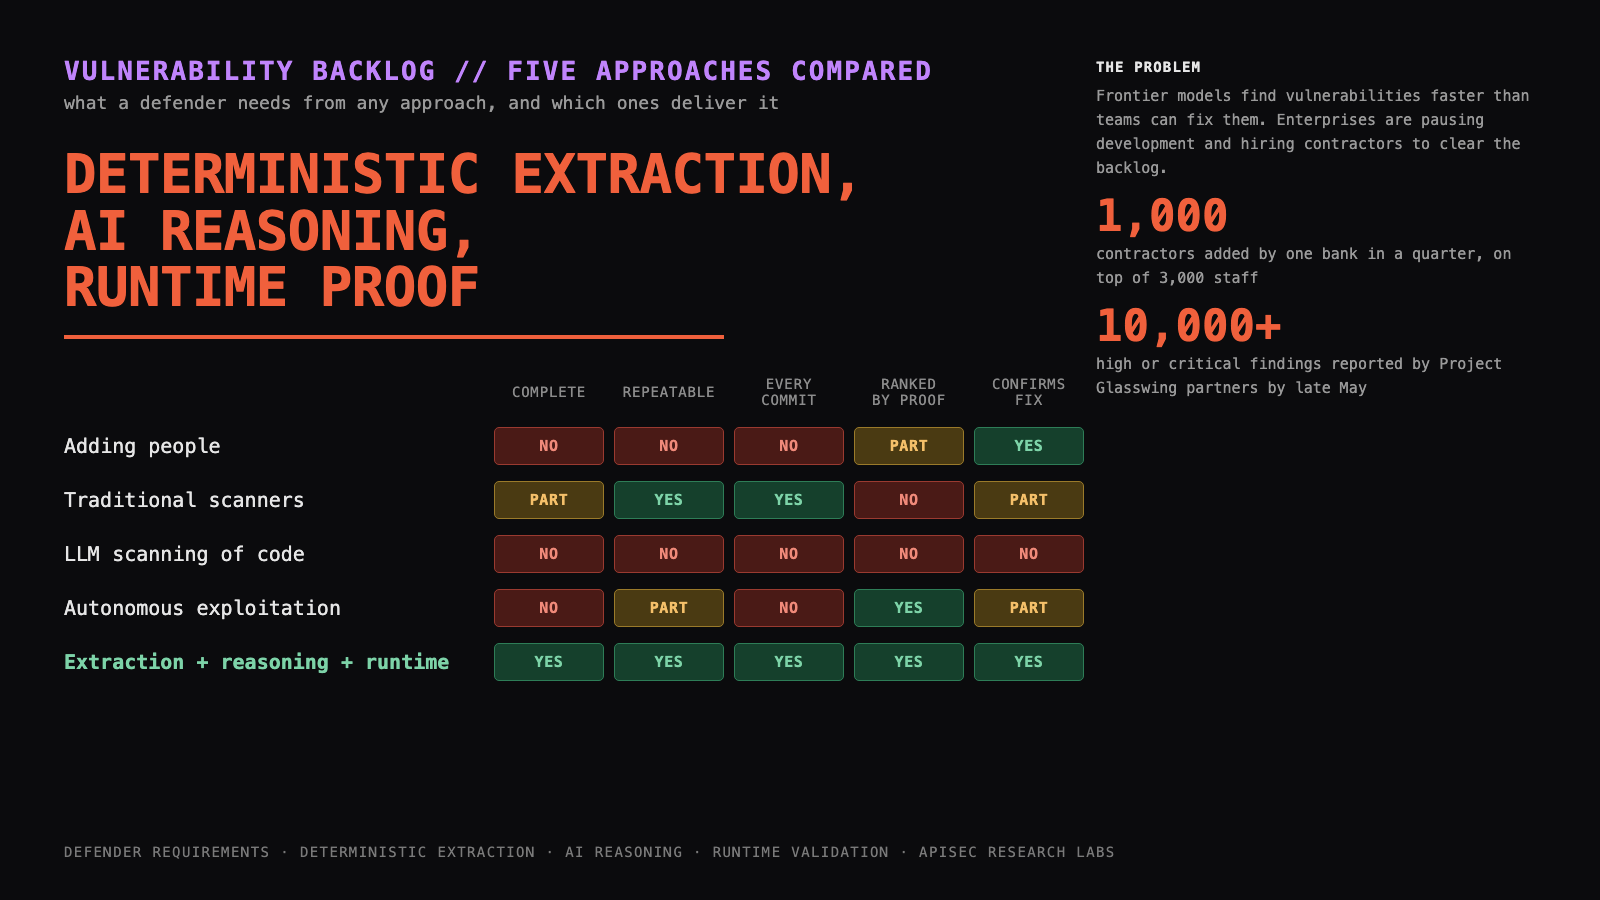
Enterprises are pausing development to fix vulnerabilities. A comparison of the approaches on the table.
· 13 min read
Rajaram Ramanathan
APIsec Research Labs

In April 2026 Anthropic released Claude Mythos Preview to a closed group of companies and government agencies under Project Glasswing, a coalition that includes AWS, Apple, Cisco, CrowdStrike, Google, JPMorganChase, Microsoft, NVIDIA and Palo Alto Networks. The model finds software vulnerabilities on its own and at scale. By late May the partners had reported more than 10,000 high or critical vulnerabilities in widely used software, and a review of a sample of those findings by Anthropic and six independent security firms confirmed more than 90 percent of them as real. Anthropic has kept the model restricted and has described the ease of finding vulnerabilities, compared with the difficulty of fixing them, as the main challenge now facing cybersecurity.
ZOOMSDAY: What Happens When Exploits Outrun Patches?

· 5 min read
Bandana Kaur
APISec Research Labs

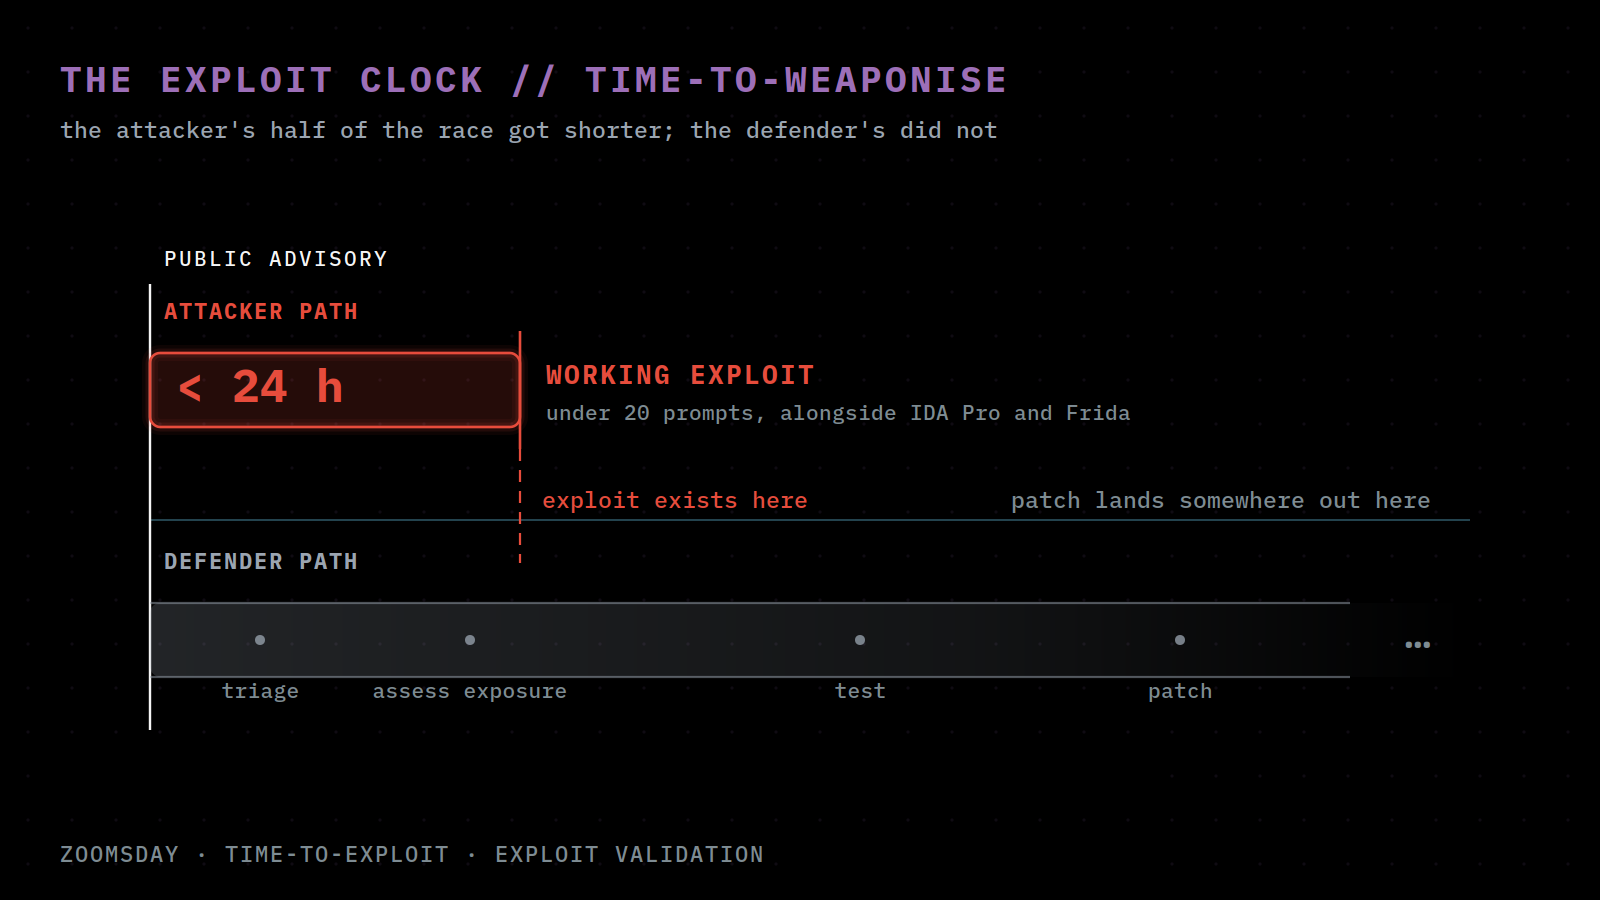
A vulnerability as severe as remote code execution can go from public advisory to working exploit much faster than most orgs can go from triage to patch. AI compresses the amount of time and expertise required for vulnerability research, but defenders are increasingly playing a game where the attacker gets the first (and faster) move. How do we level the playing field?

Mass Assignment: The Silent Killer of Application Security

· 8 min read
José Haro Peralta
APIsec Research Labs

In March 2012, Egor Homakov performed one of the most famous exploits in application security history: he acquired write rights to Ruby on Rails's GitHub repository and committed directly to its master branch. The commit is still visible for all to see (here). How was Homakov able to do this? He exploited a vulnerability in GitHub's API that allowed him to overwrite arbitrary server-side properties. Specifically, he bound his own SSH key to the profile of another user with commit rights to Ruby on Rails's repository.

The Proxy Problem: Applying Goodhart's Law to AI-Generated Vulnerability Reports

· 10 min read
Bandana Kaur
APISec Research Labs

Over the past year, bug bounty platforms have reported a dramatic rise in AI-assisted, "slop" vulnerability submissions. Much of the discussion has centered on whether large language models are capable of discovering genuine vulnerabilities or whether they merely generate convincing-looking but ultimately meaningless reports.