
Research
Original analysis, technical findings, and emerging risk studies
Every figure traces to a public source or an open dataset. Preprints and classification scripts ship alongside the writing.
Papers and deep dives

Technical deep diveAug 2026
Broken object level authorization: from invoice IDs to AI agents
What 200 disclosed HackerOne reports say about the half of BOLA almost nobody tests. Six families, the request trace that breaks each one, and the agent surfaces where they are reappearing.
Read deep dive 28 min
Research paper25 May 2026
Broken object level authorization in the wild: an empirical taxonomy from 100+ bug bounty disclosures

Bandana Kaur
arXiv:2605.25865v1 [cs.CR]
Submitted 25 May 2026
Of 107 classified reports, 84 were confirmed in scope. Action-Level Object BOLA accounts for 41.7% of them, alongside Direct Object Reference as one of the two dominant families. Roughly 21.5% of tagged reports fall out of scope entirely.
View preprint
Field research
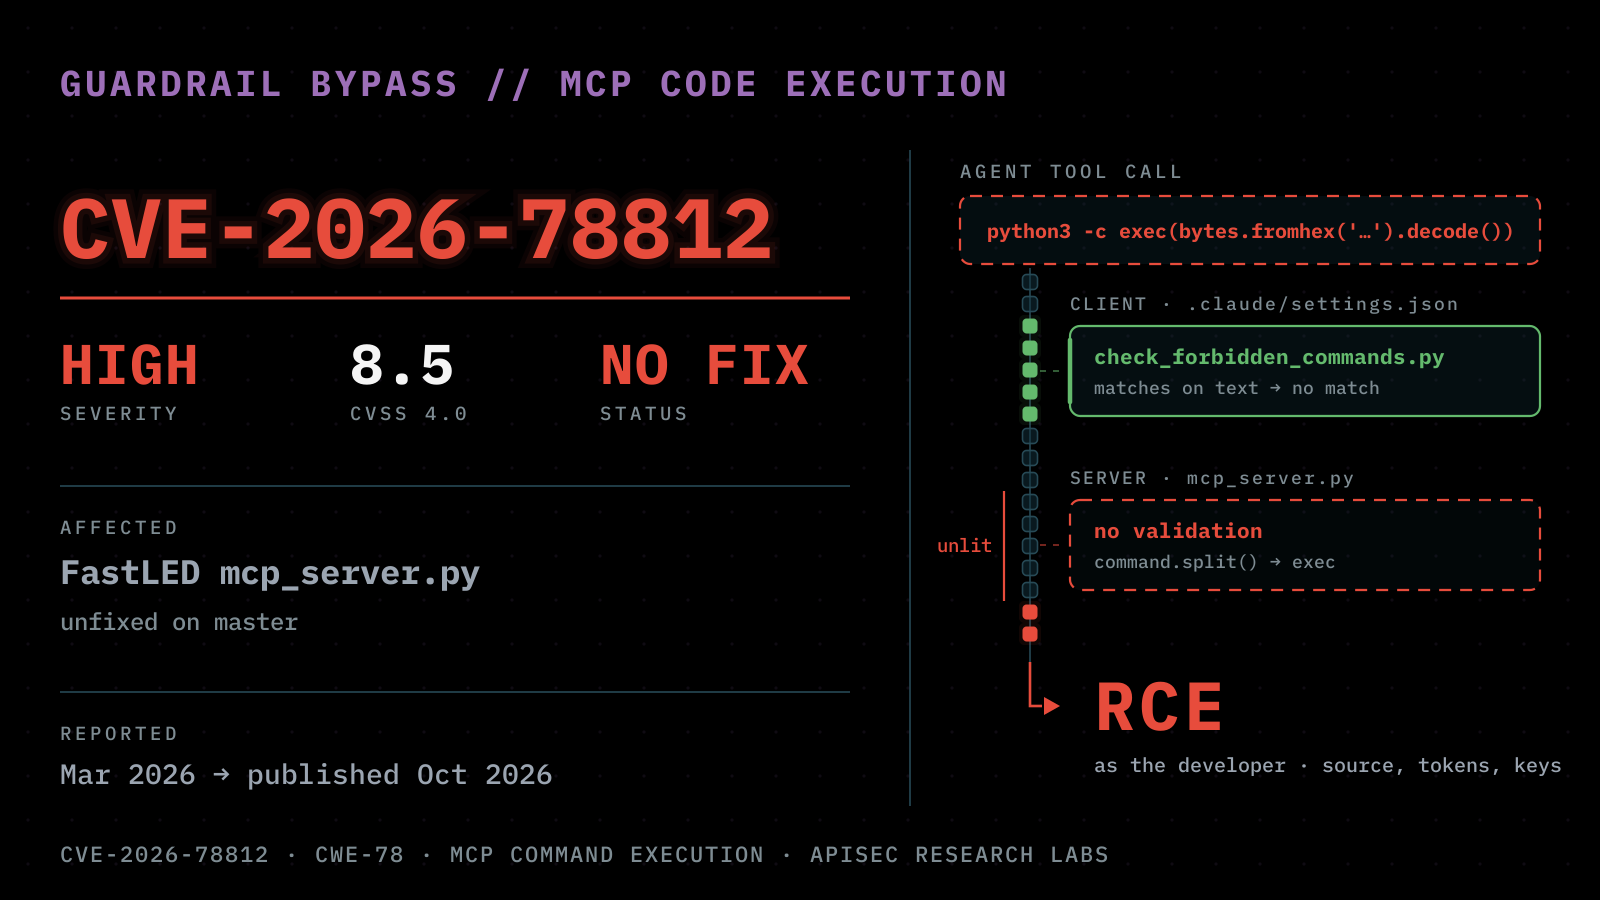
Case studyOct 2026 · 7 min
Light It Up: Agentic Guardrail Bypass to Code Execution in FastLED's MCP Server (CVE-2026-78812)
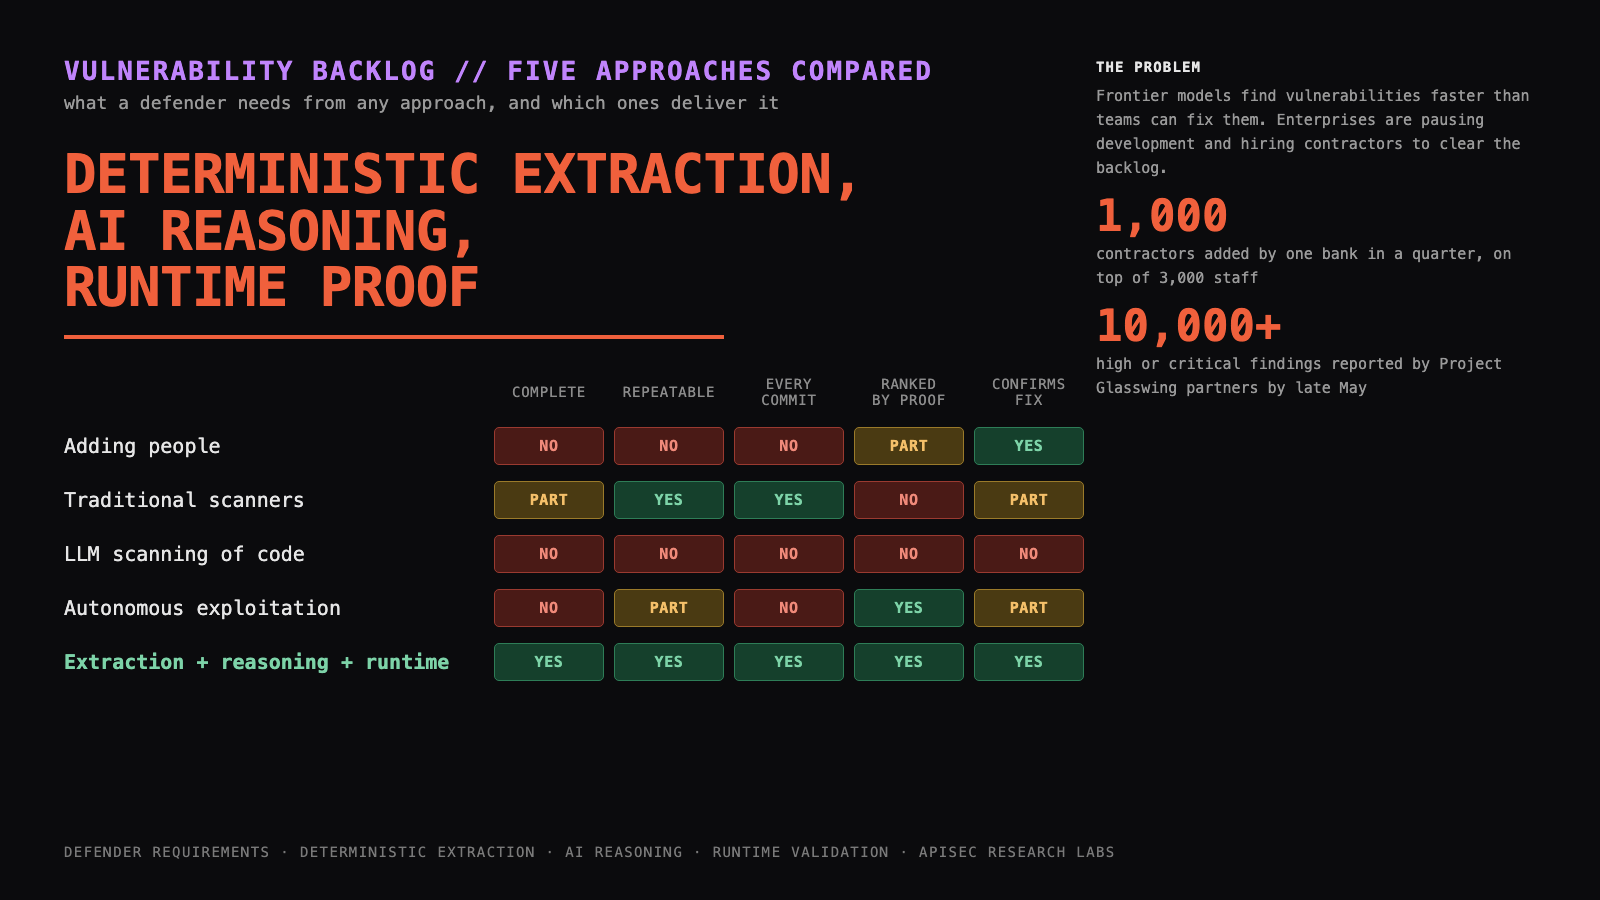
ArticleOct 2026 · 9 min
Enterprises are pausing development to fix vulnerabilities. A comparison of the approaches on the table.
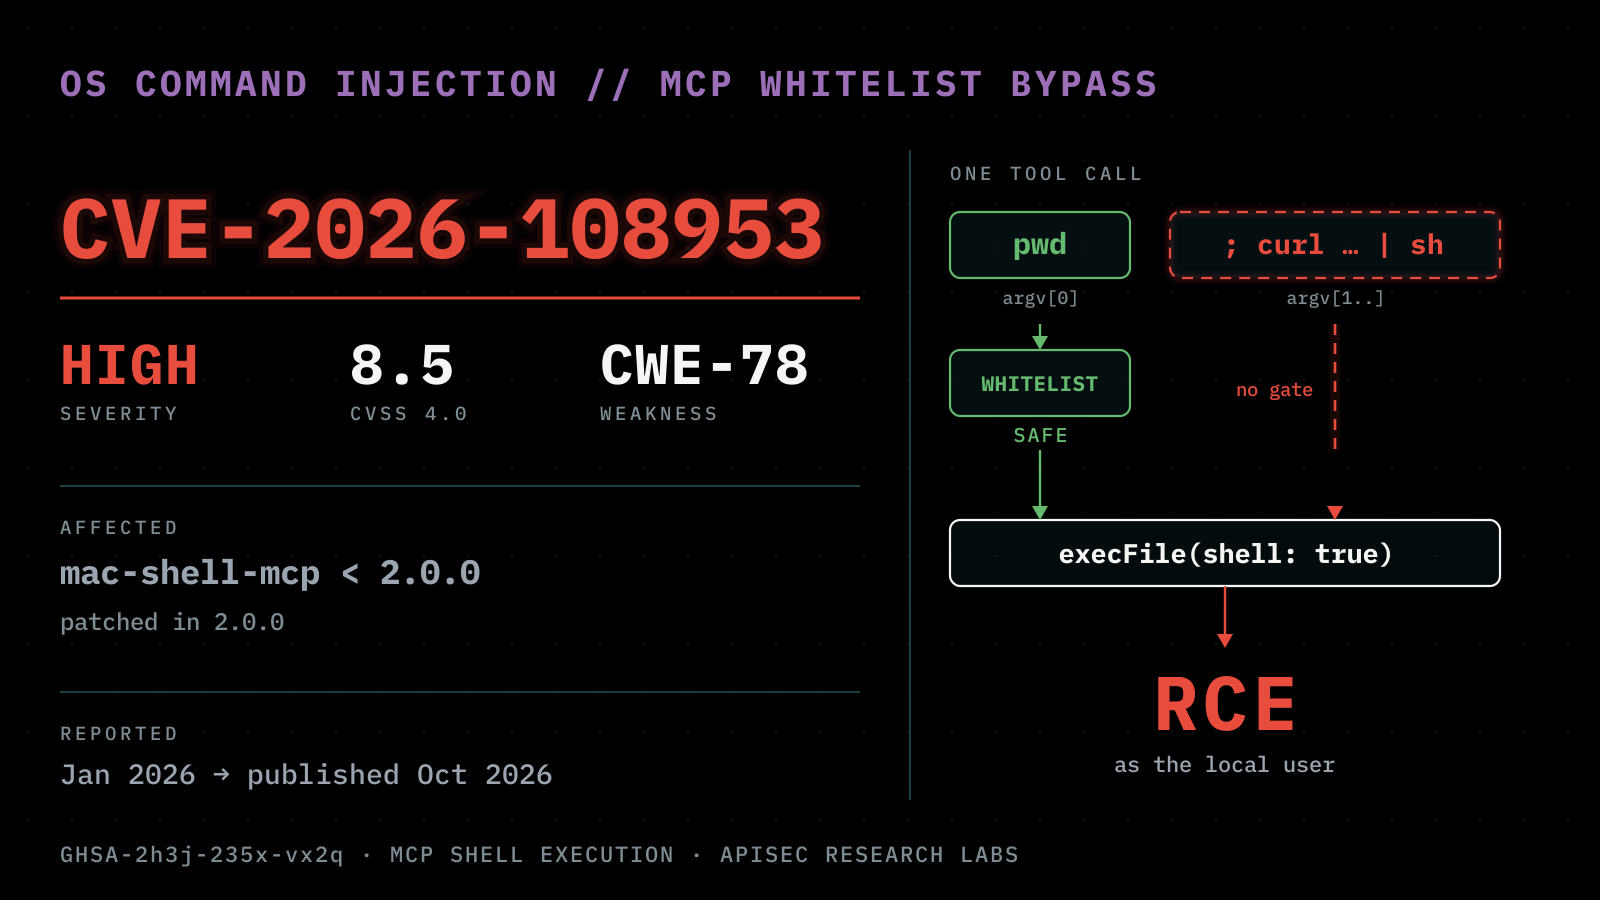
Case studyOct 2026 · 7 min
CVE-2026-108953: OS Command Injection by Whitelist Bypass in mac-shell-mcp
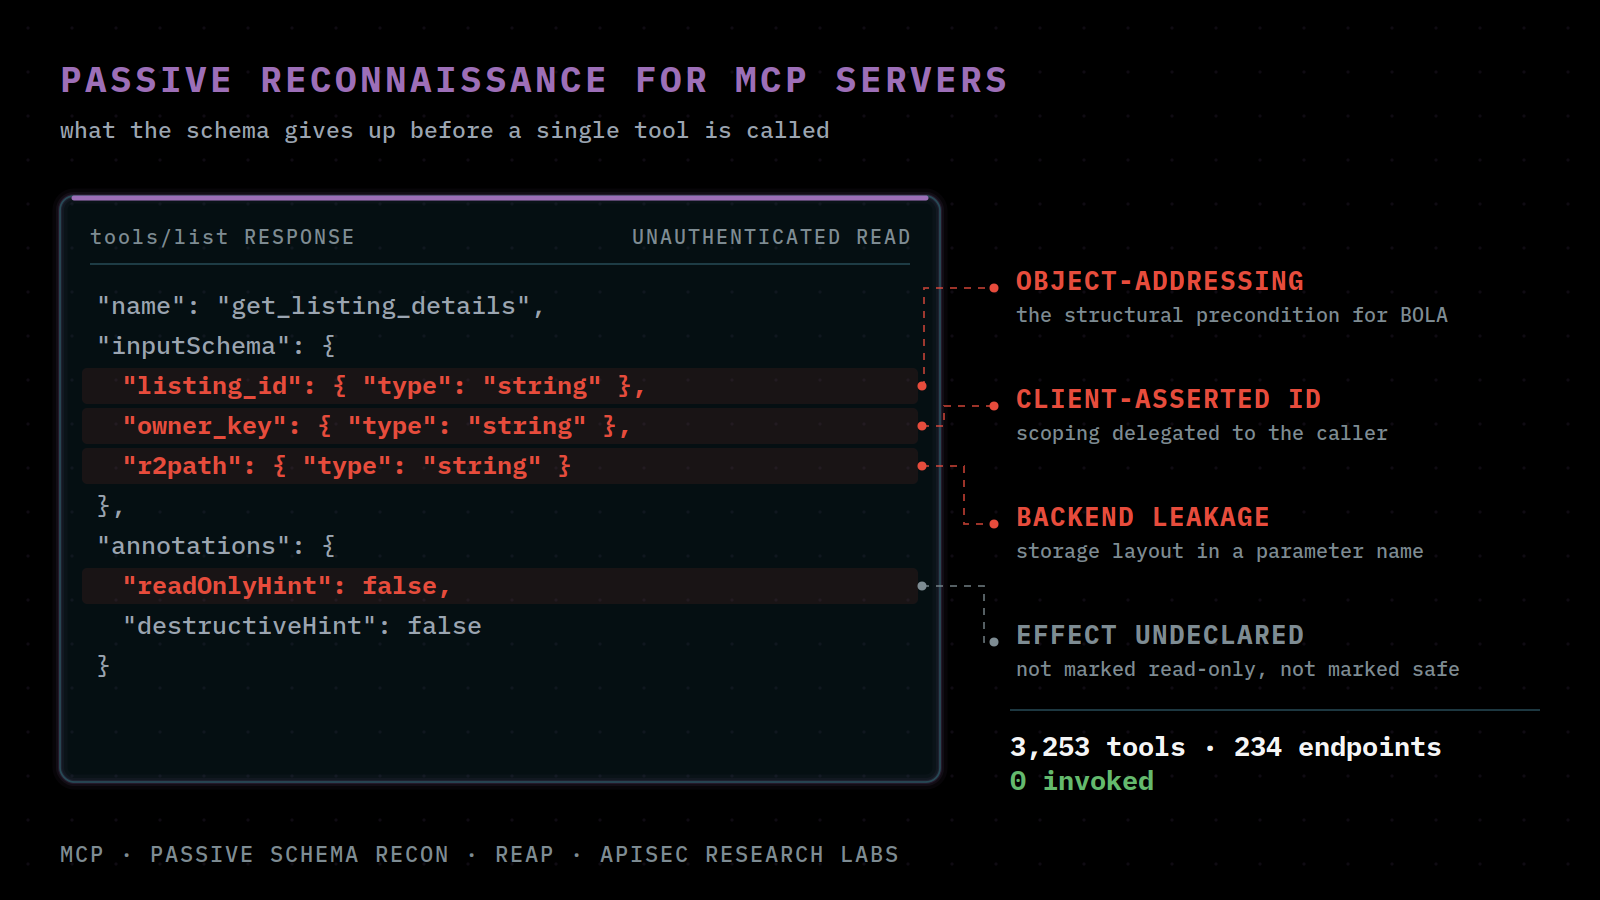
ArticleOct 2026 · 9 min
What Does Your MCP Attack Surface Look Like From the Outside?
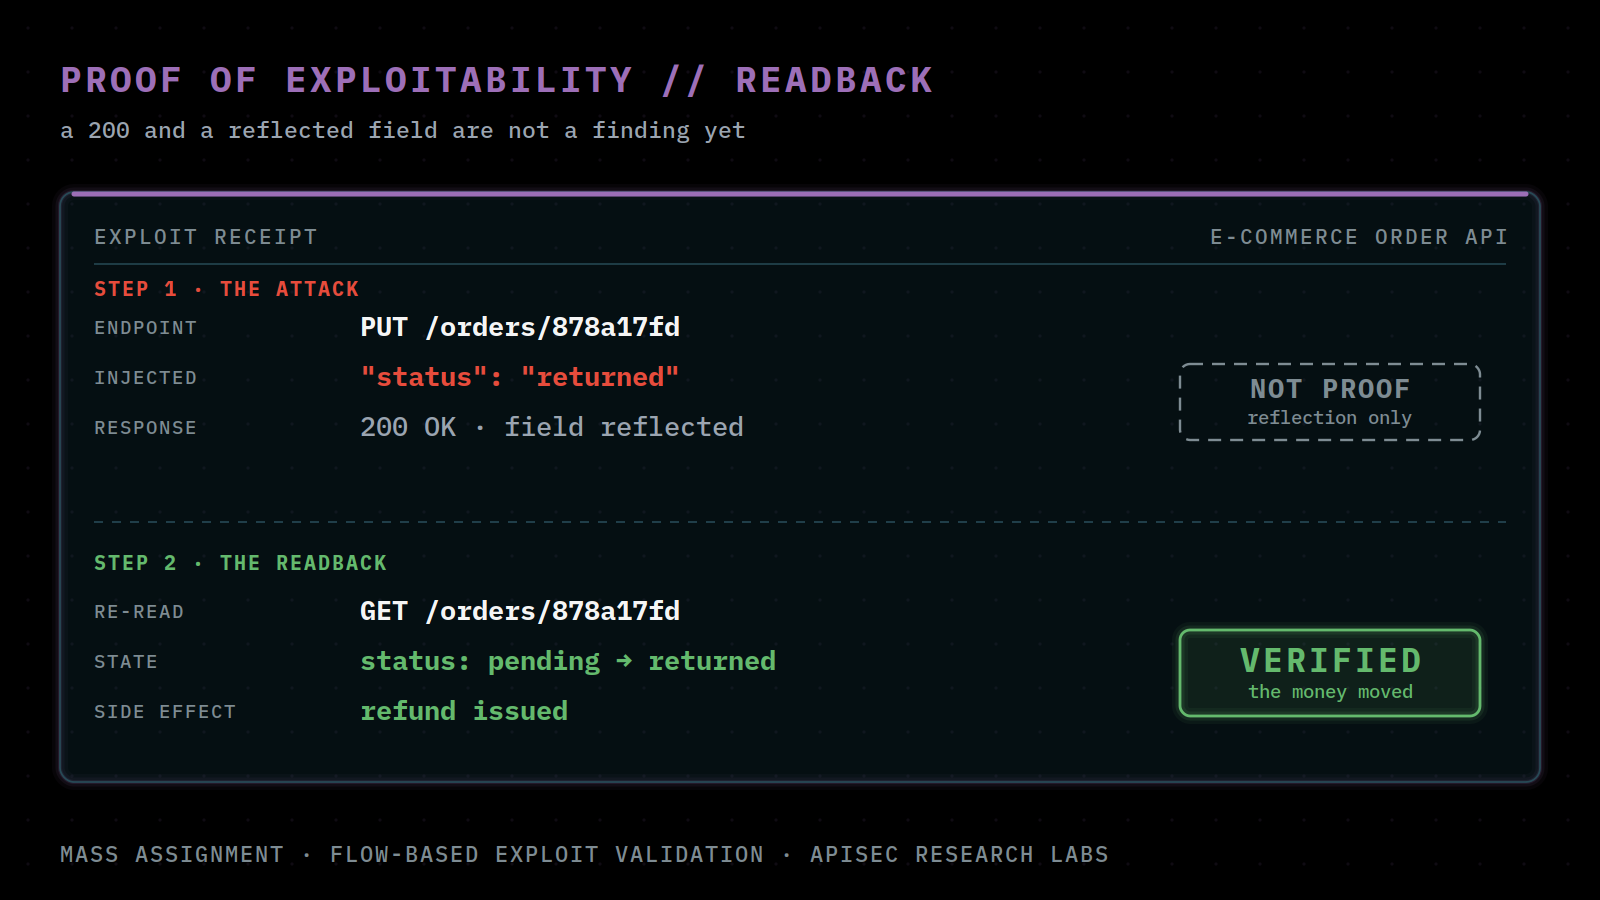
ArticleSep 2026
It's not a vulnerability until the money moves
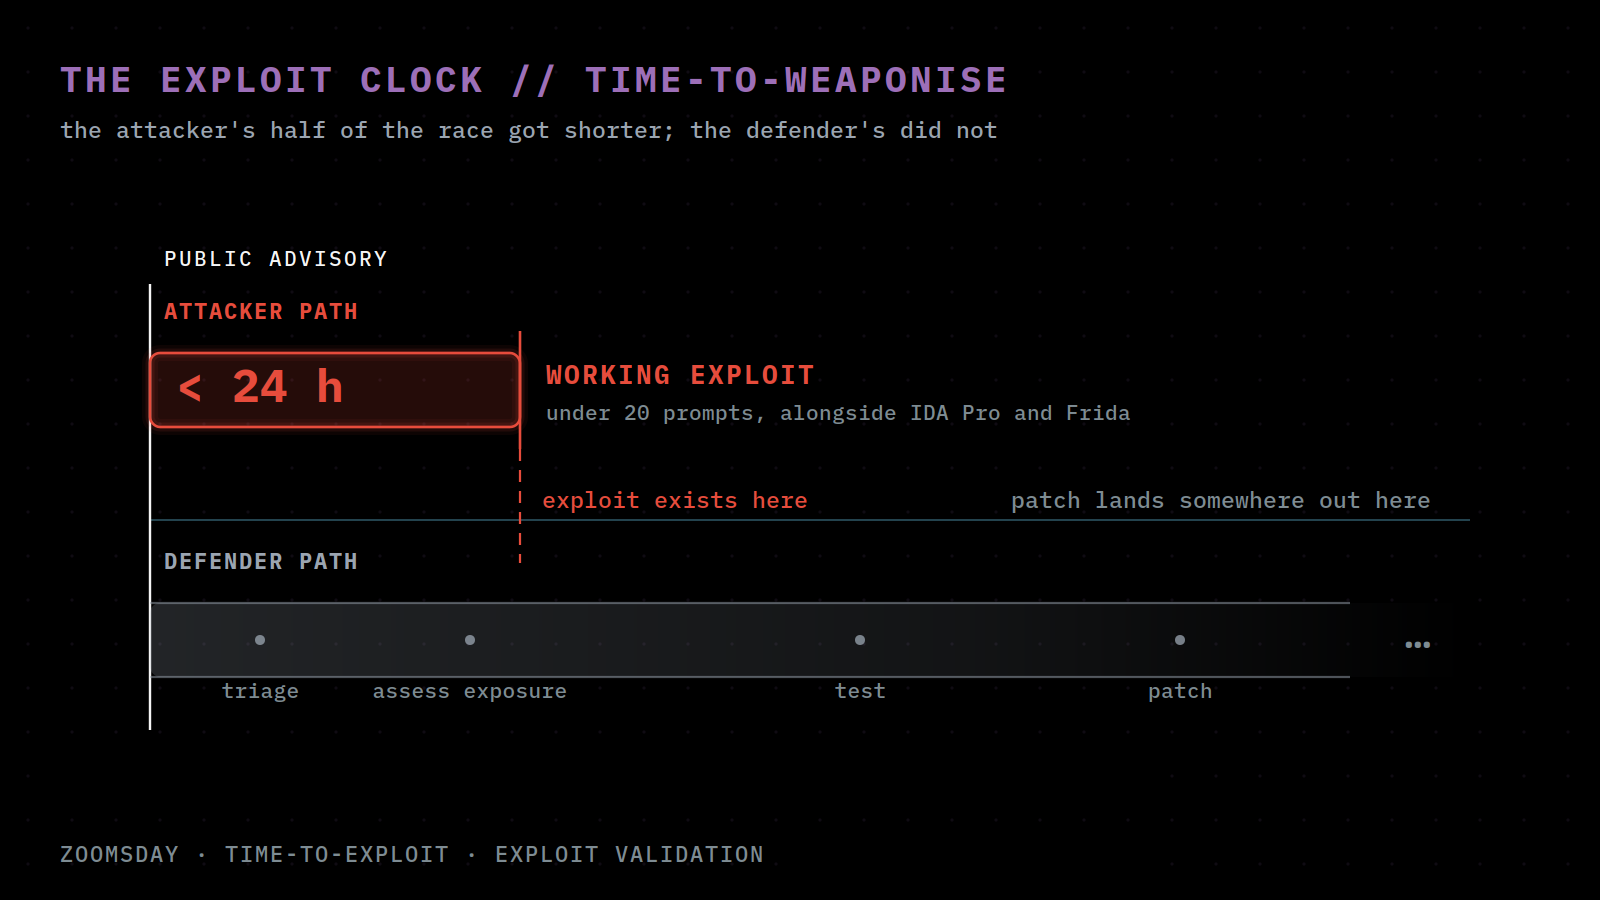
IncidentSep 2026 · 5 min
ZOOMSDAY: What Happens When Exploits Outrun Patches?
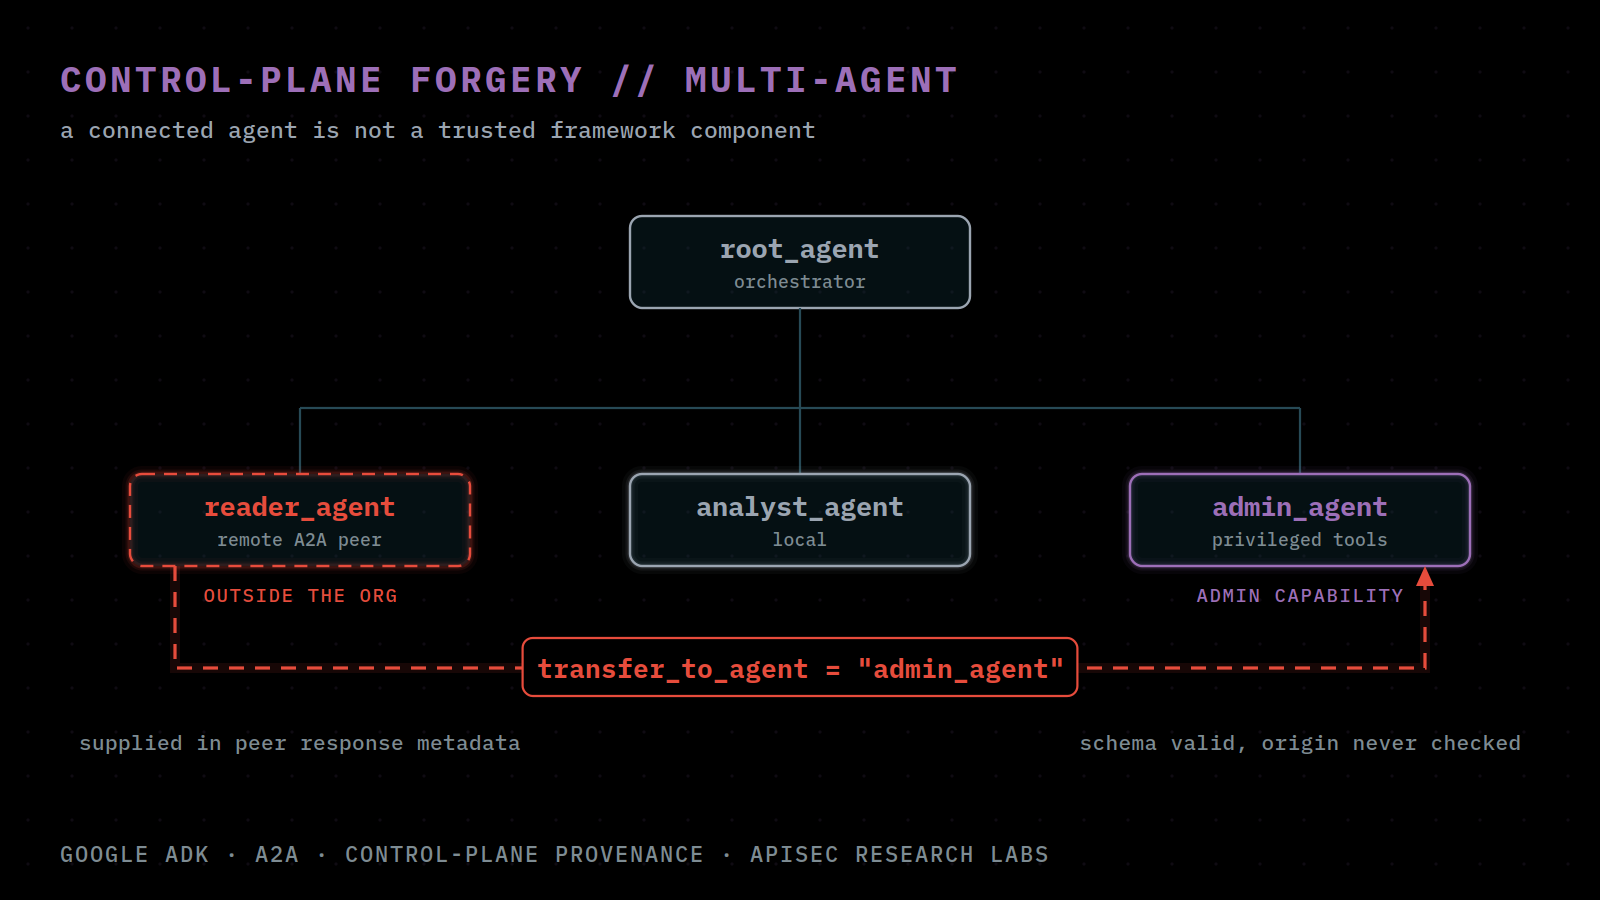
Case studySep 2026 · 9 min
Hijacking Google ADK Using Malicious A2A Peers

ArticleSep 2026 · 9 min
Observable ≠ Exploitable: The Problem With OAuth Security Measurements

Case studySep 2026 · 9 min
Trust Me, Bro: Forging Security Labels in Microsoft's FIDES Middleware

Attack chainAug 2026 · 8 min
Catfishing the Allowlist: Introducing MCP Security's Argument Injection Blind Spot

ArticleAug 2026 · 8 min
Mass Assignment: The Silent Killer of Application Security

ArticleJul 2026 · 14 min
The Seven Wonders of OAuth Exploitation

ArticleJul 2026 · 10 min
The Proxy Problem: Applying Goodhart's Law to AI-Generated Vulnerability Reports

ArticleJun 2026 · 7 min
All That Glitters Isn't Prompt Injection: Rethinking The Meta Instagram Takeover

Attack chainJun 2026 · 10 min
Beyond the $175K Bankrbot Hack: Encoding Attacks Across Layers of the Agentic AI Stack

ArticleMay 2026 · 8 min
What 100+ BOLA Reports Taught Us About Where Object-Level Authorization Actually Fails

Attack chainMay 2026 · 7 min
Prompt In, Shell Out: Exploiting GitHub AI Toolchains

Case studyApr 2026 · 8 min