
THREAT_INTEL
API Layer Attacks Report
RESEARCH
Real-World BOLA Empirical Analysis
TOOL
APIsec Bolt Code Discovery
NEW
Beyond the $175K Bankrbot Hack
RESEARCH
The Ghost in the Shopping Cart
TOOL
APIsec Bolt Browser Extension
TOOL
MCP Audit v1.0
RESEARCH
Prompt In, Shell Out
THREAT_INTEL
API Layer Attacks Report
RESEARCH
Real-World BOLA Empirical Analysis
TOOL
APIsec Bolt Code Discovery
NEW
Beyond the $175K Bankrbot Hack
RESEARCH
The Ghost in the Shopping Cart
TOOL
APIsec Bolt Browser Extension
TOOL
MCP Audit v1.0
RESEARCH
Prompt In, Shell Out
THREAT_INTEL
API Layer Attacks Report
RESEARCH
Real-World BOLA Empirical Analysis
TOOL
APIsec Bolt Code Discovery
NEW
Beyond the $175K Bankrbot Hack
RESEARCH
The Ghost in the Shopping Cart
TOOL
APIsec Bolt Browser Extension
TOOL
MCP Audit v1.0
RESEARCH
Prompt In, Shell Out
THREAT_INTEL
API Layer Attacks Report
RESEARCH
Real-World BOLA Empirical Analysis
TOOL
APIsec Bolt Code Discovery
NEW
Beyond the $175K Bankrbot Hack
RESEARCH
The Ghost in the Shopping Cart
TOOL
APIsec Bolt Browser Extension
TOOL
MCP Audit v1.0
RESEARCH
Prompt In, Shell Out
Latest Publications
Original analysis, technical findings, and emerging risk studies.
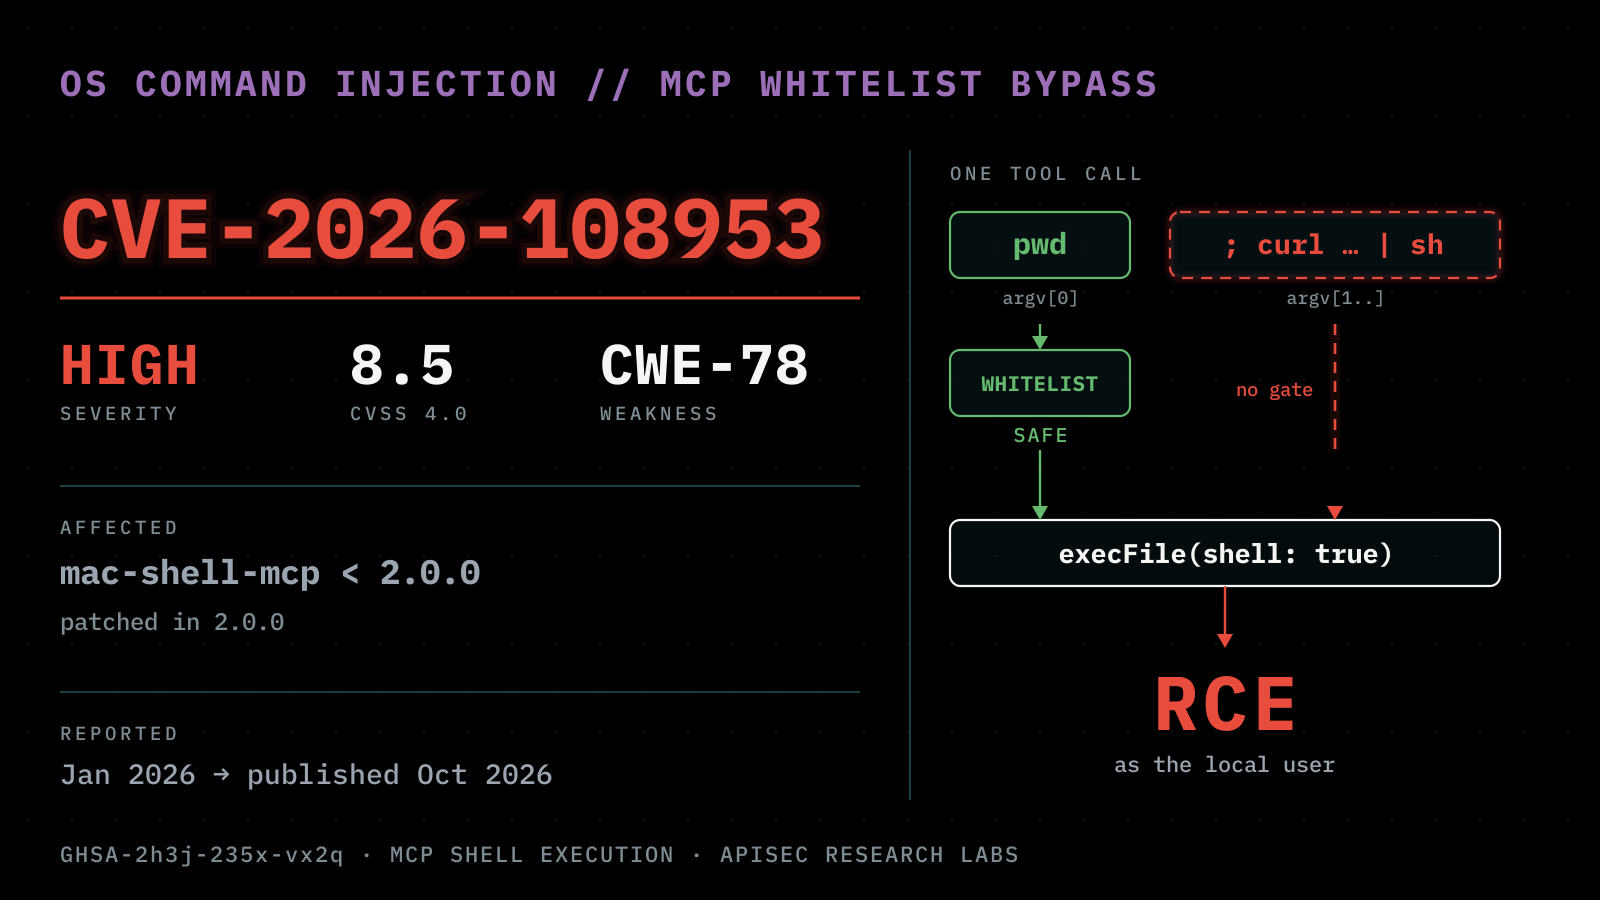
Oct 2026
CVE-2026-108953: OS Command Injection by Whitelist Bypass in mac-shell-mcp
mac-shell-mcp gives AI agents a whitelisted shell on macOS. Because execFile ran with shell: true, calling a safe command like pwd and appending shell metacharacters in the arguments slipped a second command past the whitelist, straight to RCE as the local user.
Read full report
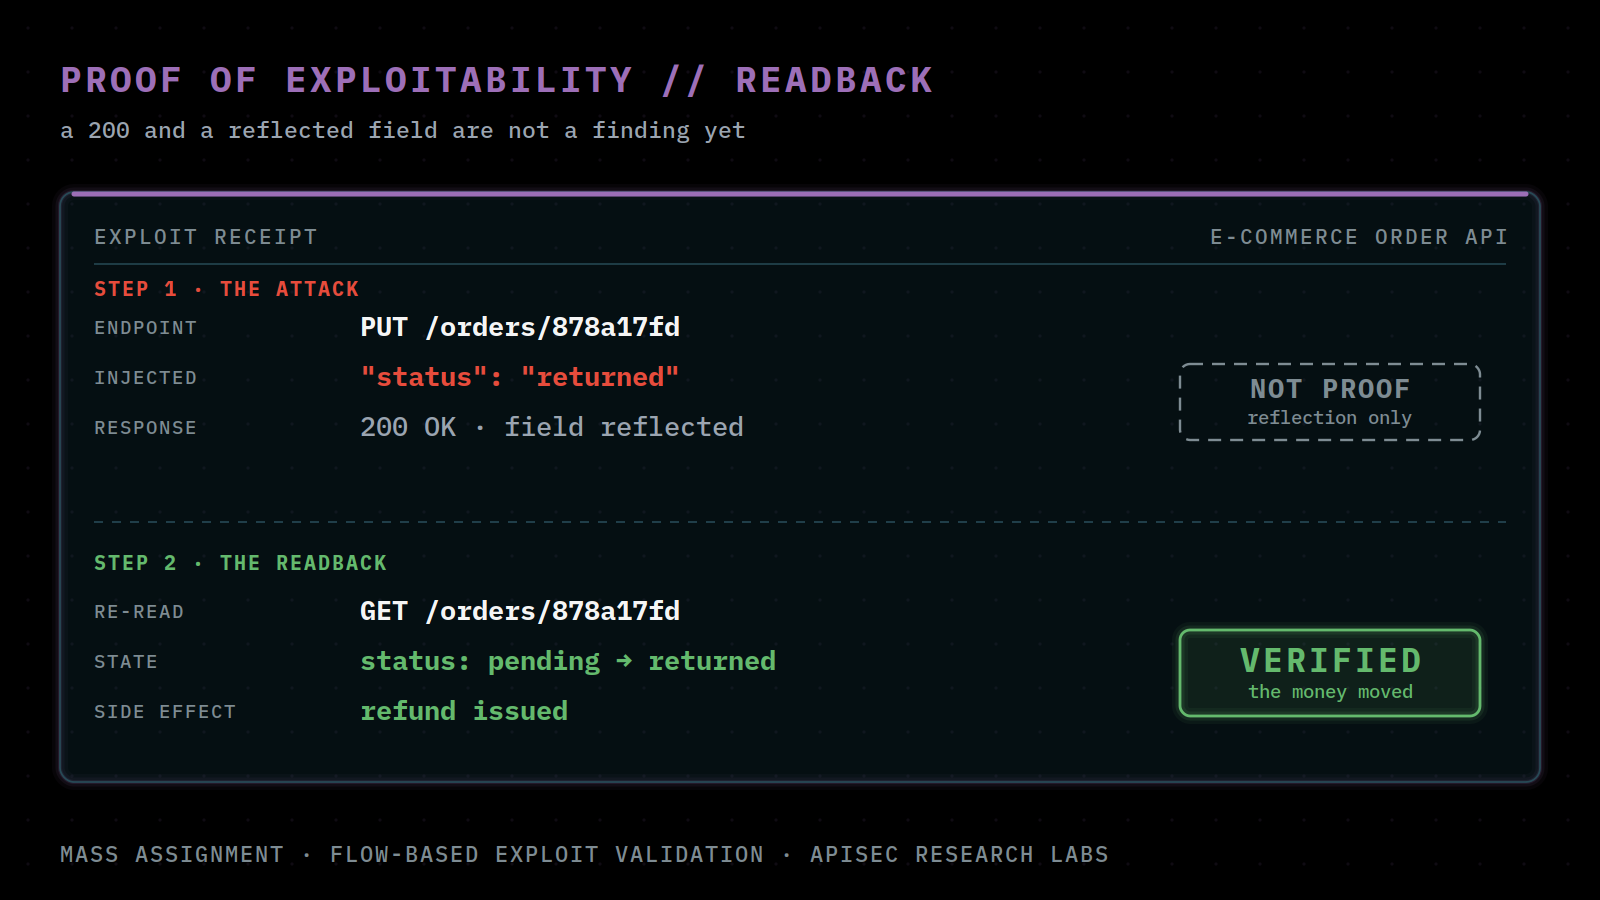
Sep 2026
It's not a vulnerability until the money moves
A 200 and a reflected value don't prove a mass assignment exploit. Real proof of exploitability means confirming the side-effect: reading back the state or exercising the flow. Here's why that's hard for scanners, and how APISec solves it.
Read full report
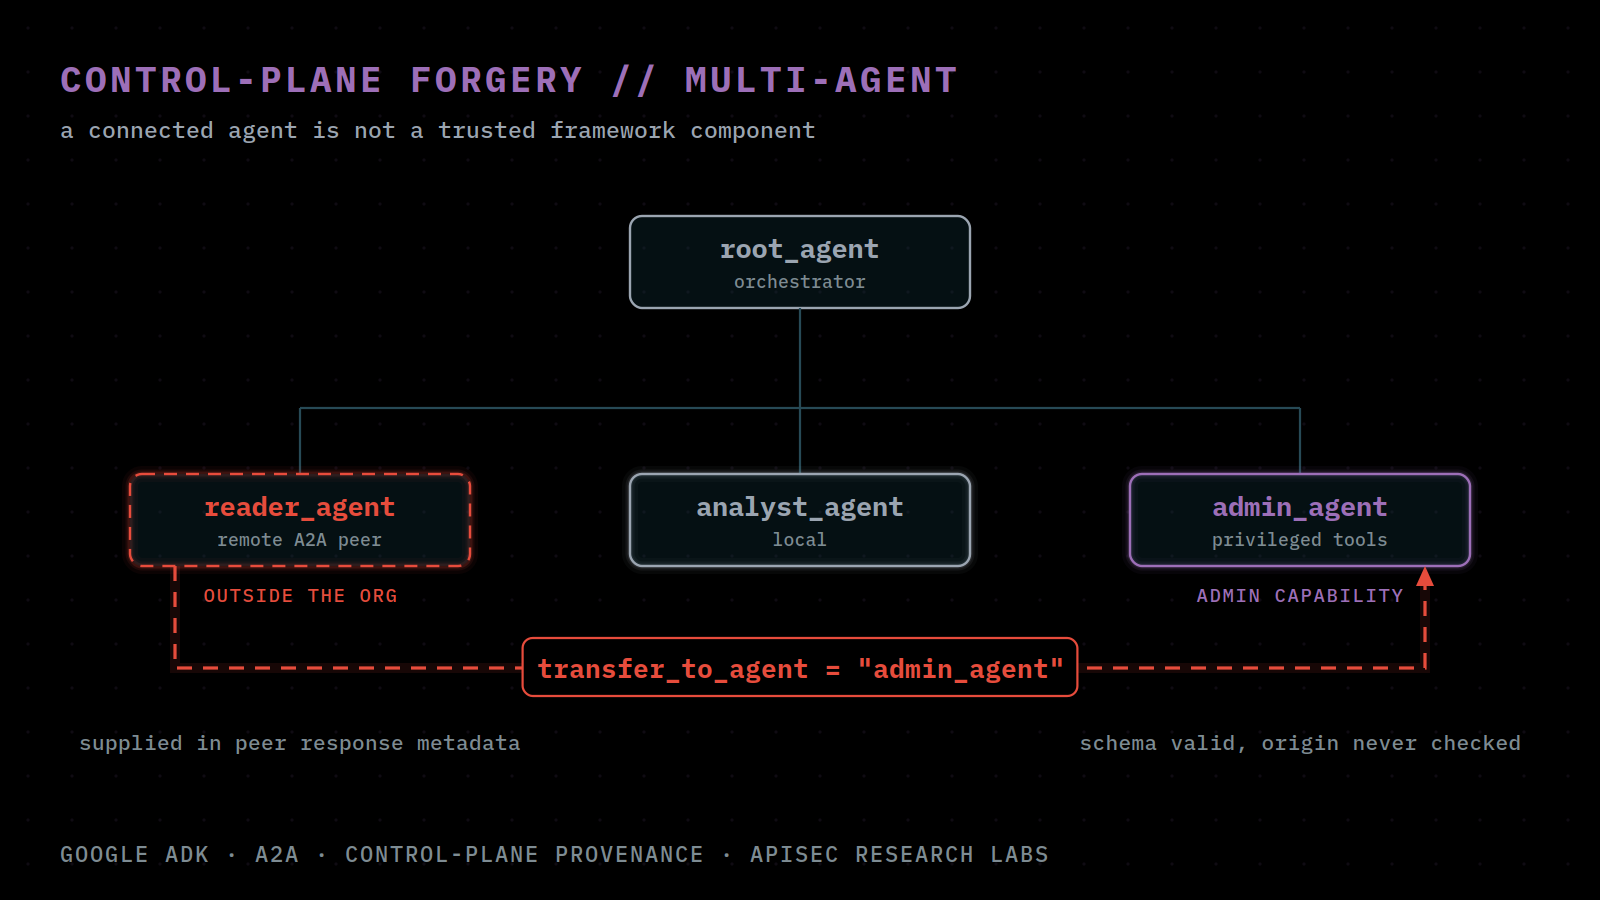
Sep 2026
Hijacking Google ADK Using Malicious A2A Peers
A remote A2A peer in Google's Agent Development Kit can forge the framework's own control-plane object, EventActions, and use it to redirect execution to higher-privileged sibling agents, rewrite session state, and rewind the conversation history the model relies on for safety instructions. No signature or origin check sits between a peer's metadata and framework state.
Read full report

Sep 2026
Observable ≠ Exploitable: The Problem With OAuth Security Measurements
A crawl of the Tranco top-10,000 found 3,148 authorization requests missing PKCE. We tried to actually exploit what we measured, and the gap between 'observable' and 'exploitable' turned out far larger, and stranger, than the count suggests.
Read full report
THE STATE OF APPLICATION SECURITY
The numbers don't lie.
0K+
CVEs in 2025
0%
Increase from 2023
0%
AI code fails benchmarks
0%
Ship known vulns
Sources: CVE Data Review 2025 • Veracode • Black Duck DevSecOps Report • Checkmarx
Built for Practitioners
APIsec Bolt Browser Extension
Discover your full API attack surface directly from your browser: no proxies, agents, or setup required. As you interact with any web application, Bolt captures live API traffic, filters out noise, and builds a real-time inventory of endpoints and parameters. Export clean OpenAPI specs in one click and send APIs straight to APIsec.ai for automated security testing.
APIsec Bolt Code Discovery
Find every API endpoint hiding in your source code before it ships. This GitHub Action scans your repository at commit or on a schedule, automatically detects frameworks (Spring Boot, FastAPI, Flask, ASP.NET Core, and more), generates an OpenAPI 3.0 specification from your code, and raises a pull request with the results. Shift API discovery left and catch undocumented and shadow endpoints in the CI/CD pipeline, not in production.
MCP audit
See what your AI agents can actually access before attackers do. Scan Model Context Protocol configurations for exposed secrets, shadow APIs, and undeclared AI models, then generate AI-BOMs for compliance and governance. MCP Audit maps your agent trust boundaries so you can identify misconfigurations and over-permissioned connections across your AI infrastructure.
AI Surface
Find and govern the AI surfaces in your application code at PR time. AI Surface is a static source-code analyzer that detects LLM SDK call sites across 12 providers, agent frameworks like LangChain, LangGraph, and CrewAI, MCP servers, model gateways, and AI infrastructure — flagging 13 risk indicators including financial actions, destructive operations, broad permissions, and exposed provider API keys. Runs 100% locally with no network calls or telemetry, ships as a GitHub Action with sticky PR diff comments, and supports baseline mode to track only newly introduced AI surfaces. Make your AI attack surface visible to the security team before attackers find it.
APIsec Skills
Make your AI coding assistant write secure APIs by default. Five always-on rules and six on-demand skills put the OWASP API Security Top 10 inside Claude Code, Cursor, GitHub Copilot, OpenAI Codex, Gemini CLI and Windsurf. There is nothing to configure, and nothing leaves your machine.
FREE NEWSLETTER
The Labs Dispatch
Subscribe to our newsletter and be the first to hear about new tools, get the latest updates on our research, and receive curated articles you would actually want to read.
Free forever. Unsubscribe anytime. We never share your email.